Inside the Web-Based Apple Pay Scam Exploiting Mobile Browser Visuals
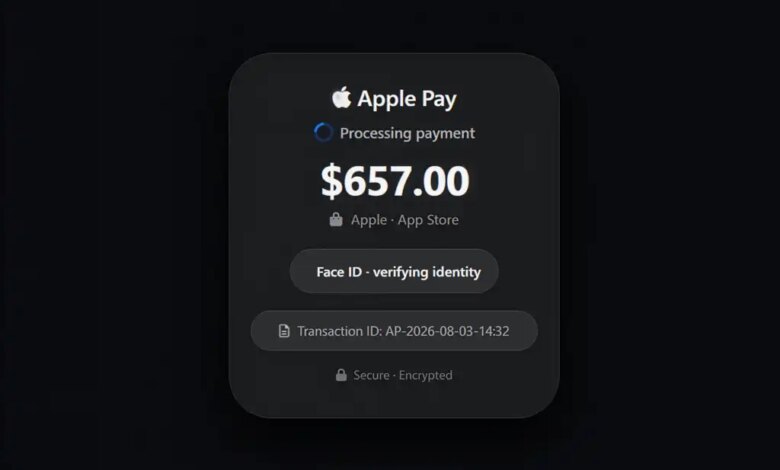
A sophisticated social engineering scam operating through standard web browsers is actively targeting mobile users by mimicking official Apple Pay system notifications and purchase receipts. By combining simulated system animations, hardcoded order details, and automated voice warnings, the threat vectors aim to trick victims into believing an unauthorized charge of $657 has been processed against their account. The ultimate objective of the campaign is not technical exploitation of the iOS operating system, but rather psychological manipulation designed to force users into calling a fraudulent tech support hotline.
While the visual elements closely imitate native iOS components—including animated Face ID graphics and security iconography—the underlying mechanism relies entirely on conventional website code. Understanding how this illusion is constructed, why its security claims are false, and how to safely exit the browser tab provides essential protection against this evolving web threat.
Anatomy of the Visual Illusion
The core of the attack rests on high-fidelity visual impersonation. When a user lands on an compromised or malicious webpage, the site renders a sequence of user interface elements designed to look like a native system alert from Apple. To the untrained eye, the display appears to show an active Apple Pay transaction in progress.
The webpage displays several specific graphical prompts to establish legitimacy:
- Simulated Face ID Animation: A graphic mimicking the native iOS biometric scan visual plays on the screen, creating the impression that a security check has just been executed.
- Security Graphics: An animated padlock unlocking visual appears, suggesting an authenticated digital transaction.
- Formatted Receipt Layout: A structured transaction record displays an order for $657 attributed to the App Store, complete with a realistic-looking transaction ID.
- Support Call Prompts: A prominent phone number is displayed alongside a button encouraging the user to “View Details” or reach out to “Apple Support.”
Despite the realistic presentation, none of these components interact with the underlying device firmware or authentic Apple services. There is no connection to the user’s actual Apple ID, no active session with Apple Pay, and no real financial transaction taking place on the device. The entire sequence consists exclusively of browser-rendered images, cascading style sheets (CSS) animations, and JavaScript routines.
Audio Escalation and Manufactured Urgency
To convert visual panic into immediate action, the scam incorporates automated audio triggers. If a visitor taps the “View Details” button on the fake receipt, the webpage invokes a web audio script that plays a localized voice alert. The recording states: “Unauthorized charge of six hundred fifty-seven dollars from your Apple ID. Please call support immediately.”
The inclusion of explicit audio commentary serves a tactical purpose in social engineering. In a standard browsing environment, unexpected voice playback breaks the user’s analytical focus and heightened emotional stress. By explicitly mentioning a specific, high-dollar amount—$657—the scam triggers an immediate reflex to cancel or dispute the charge before checking authentic banking channels.
Crucially, the data driving this experience is static. Every target who reaches the fraudulent domain sees the exact same transaction ID, the exact same $657 fee, and hears the identical audio recording. The uniformity of these details highlights that the page possesses no individualized data about the visitor’s actual financial accounts or identity.
Browser Interception and Exit Lockout Tactics
When users recognize something is amiss and attempt to navigate away using the browser’s back button, the website deploys secondary defense mechanisms to keep the target engaged. The script triggers a browser dialog box claiming that an “Apple ID session is active” and warns that leaving the page could expose payment and banking details to severe security risks.
This claim is entirely fabricated. Within standard web architecture, a public webpage has no technical capability to monitor, manage, or hold open an active “Apple ID session” on a user’s phone. Furthermore, navigating away from a website or closing a browser tab cannot expose local banking data to external threats. The warning prompt utilizes standard JavaScript alert handlers designed to create friction, confusing the user into remaining on the domain where the fraudulent phone number remains displayed.
Comparing Fake Web Scams with Authentic System Behaviors
Distinguishing between web-based trickery and legitimate system notifications relies on identifying where and how alerts are rendered on a mobile device. Native operating system notifications behave distinctly from elements contained within a web browser tab.
| Security Feature / Aspect | Web-Based Scam Page | Authentic Apple System / Service |
|---|---|---|
| Alert Location | Renders strictly inside the browser viewport (Safari, Chrome, etc.). | Appears as a native iOS system banner or within the dedicated Wallet app. |
| Transaction Uniformity | Displays a static $657 charge and identical transaction ID for all users. | Generates unique transaction details visible inside Wallet or official email receipts. |
| Audio Indicators | Triggers automatic voice recordings asking the user to dial a phone number. | Uses standard system alert tones; never broadcasts spoken phone prompts. |
| Support Escalation | Demands an immediate phone call to an displayed, unverified helpline. | Directs users to official support channels via support.apple.com or standard app settings. |
| Navigation Control | Displays warning pop-ups about “active sessions” when pressing the back button. | Allows seamless navigation within system menus without lock-up dialogs. |
Recommended Response and Safe Remediation
If an individual encounters one of these pop-up scams while browsing, the most effective response is immediate disengagement. Engaging with any button on the page—including “Cancel,” “View Details,” or exit dialogs—can trigger additional pop-ups or audio files.
To safely clear the malicious page, users should follow these steps:
- Avoid Interactive Elements: Do not tap any buttons, links, or pop-up options displayed on the page.
- Do Not Call the Number: Under no circumstances should the phone number displayed on the screen or spoken in the audio alert be dialed.
- Access Browser Tab Overview: On an iPhone using Safari, tap the tab view button located in the bottom-right corner of the interface.
- Force Close the Tab: Tap the “X” on the thumbnail preview or swipe the tab away to close it completely.
- Clear History if Needed: If the scam page repeatedly reopens upon launching the browser, navigate to the device Settings menu, select Safari, and execute “Clear History and Website Data.”
The Broader Threat Context
This campaign reflects a broader trend in tech support fraud, where malicious actors trade complex software exploits for convincing interface design. By exploiting the visual trust users place in familiar system components like Apple Pay and Face ID, cybercriminals attempt to bridge the gap between web advertising networks and direct phone-based scam centers.
Recognizing that web pages operating inside a browser tab cannot access native device security features or process unauthorized payment charges without explicit system prompts remains the strongest line of defense against browser-based social engineering.